By Olivia Parker
The United Kingdom is likely to confront destructive AI cyberattacks targeting its critical national infrastructure by 2028 as criminal syndicates and hostile states increasingly weaponize artificial intelligence, Britain’s cyber chief warned on Tuesday, November 3, 2026. Officials urged public utilities and businesses to overhaul outdated defenses before automated threats trigger real-world disruptions.
Escalating Threats to Physical Infrastructure
Speaking at the release of the annual report from the National Cyber Security Centre (NCSC), agency head Richard Horne cautioned that artificial intelligence will allow long-ignored software weaknesses to be exploited at an unprecedented scale. He noted that AI-driven malware and ransomware will rapidly target organizations that have delayed essential security upgrades.
Horne warned that executives who have relied on cheap, outdated systems could soon be forced to explain why store shelves are empty, lights are out, or companies have collapsed. Modern Technology directly controls essential physical operations, including electricity switching, water facility sluice gates, dam controls, factory assembly lines, heating networks, and commercial refrigeration.
To illustrate the vulnerability of civilian systems, Horne pointed to recent cyber intrusions that disabled supermarket refrigeration units in France. The NCSC assessment concluded that while artificial intelligence is more likely to amplify and speed up existing hacking tactics than invent entirely new vulnerability classes, it will substantially raise the volume and efficiency of hostile campaigns.
State-Sponsored Operations and Geopolitical Rivals
According to the NCSC annual report, Chinese cyber operations represent the most sophisticated and sustained digital challenge currently confronting Britain. Intelligence analysts expect both China and Russia to routinely integrate artificial intelligence into their cyber toolkits to advance their strategic and geopolitical objectives over the coming years.
Horne observed that Moscow intentionally wages digital campaigns designed to stay just below the threshold of armed military conflict, while Iran continues to launch cyber operations against British targets and dissidents perceived as threats to Tehran. European networks have already experienced severe state-linked sabotage targeting essential winter energy supplies.
British and European Union authorities previously attributed a December 2025 cyberattack against Poland’s national energy grid to Russia’s FSB security service. Officials noted that had the December 2025 intrusion succeeded, approximately 500,000 people in Poland could have been left without electricity during freezing winter conditions.
Billions in Economic Losses Prompt Urgent Call
The NCSC estimated that malicious cyber activity currently costs organizations across the United Kingdom nearly $20 billion every year. In one high-profile 2025 incident, automaker Jaguar Land Rover suffered more than $260 million in direct financial losses after a cyberattack disrupted its production and rippled through its supply chain, weighing on the broader British economy.
Anne Keast-Butler, director of Britain’s signals intelligence agency GCHQ, which oversees the NCSC, stressed that every British organization must act immediately. She emphasized that corporate cybersecurity is no longer merely about protecting customer accounts and company revenues, but now serves as a front-line defense for the entire nation.
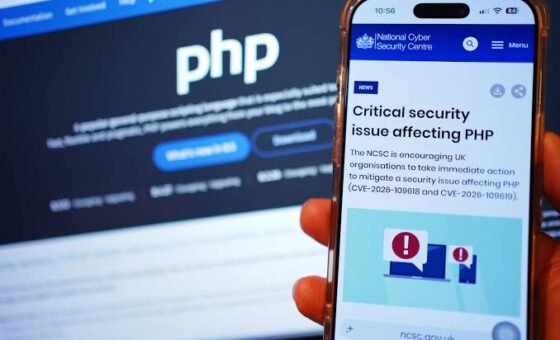
The warnings also follow an international scramble in late October 2026 to patch two AI-discovered flaws in the PHP programming language used by 70% of global websites. To guard against both automated malware and state hackers, the NCSC urged organizations to keep all devices patched, restrict administrator privileges, and maintain offline data backups.